
Execute untrusted Python code in isolated Docker containers
A self-hosted secure file system and Python execution engine for agents, with Docker/gVisor isolation, job queues, and replay built in.
0.3.0Add to Favorites
Why it matters
Run AI-generated or untrusted code safely in production by providing isolated execution environments with built-in job queuing, retry logic, execution history, and gVisor sandboxing-eliminating the need to build custom queue infrastructure, persistence layers, and security boundaries.
Outcomes
What it gets done
Execute Python code in ephemeral Docker containers with automatic cleanup and resource limits
Queue and retry failed jobs with built-in worker pools and idempotency keys
Store execution history with stdout, stderr, timing data, and artifacts in PostgreSQL
Isolate untrusted workloads using gVisor, seccomp profiles, and network-deny defaults
Source
Get it from source
Spark does not host a copy of it.
Open sourceReports
Agent outcome reports
No reports yet
Overview
TakoVM is a self-hosted execution environment that gives AI agents a secure file system and Python runtime, with job queues, PostgreSQL-backed execution history, and a replay/fork API included. Each job runs in its own Docker container with optional gVisor sandboxing. Reach for it when agents need to run untrusted, AI-generated code and you want the full job queue, history, and replay stack included rather than built on top of a bare sandbox.
What it does
TakoVM is a secure file system and Python execution environment for AI agents, with job queues and Docker isolation built in. Every job runs in its own isolated Docker container with an ephemeral workspace, optional gVisor sandboxing, job queues, retries, and execution history included. Unlike sandbox-only tools such as e2b, daytona, and microsandbox, which give isolated code execution but leave you to build a job queue, execution history, retry logic, idempotency, and replay tooling yourself, TakoVM bundles all of that: an async job queue and worker pool with no separate Redis/Celery setup, PostgreSQL-backed execution history (stdout, stderr, timing, artifacts) for every job, a rerun/fork API to replay past jobs with the exact same code and inputs, per-job Docker isolation with seccomp filtering, network isolation off by default with an optional per-job-type allowlist, and self-hosted, offline-capable, zero-per-execution-cost operation.
Isolation is layered: gVisor as a userspace kernel, per-job ephemeral Docker containers, a default-deny seccomp profile, --network=none by default, capability dropping, non-root execution, and enforced resource and input limits. The default security_mode: strict with container_runtime: runsc refuses to start a job rather than run it without the gVisor boundary; security_mode: permissive allows falling back to standard Docker (runc) on hosts without gVisor, at the cost of the userspace-kernel boundary, and is documented as unsuitable for untrusted code.
When to use - and when NOT to
Use it when agents need to execute untrusted, often AI-generated code and you want the full operational stack - job queue, execution history, retries, replay/debugging, and isolation - rather than assembling it yourself on top of a bare sandbox. It is self-hosted and offline-capable, which fits teams that want zero per-execution cost and control over the isolation boundary.
Today each container is single-use; persistent, per-agent workspaces that rehydrate across runs are on the roadmap, not yet shipped. Do not run untrusted code under security_mode: permissive - that mode's runc fallback removes the gVisor userspace-kernel boundary and is intended for hosts without gVisor (local development or CI), not production isolation.
Inputs and outputs
Input is code submitted via the REST API or the Python SDK, for example curl -X POST http://localhost:8000/execute -d '{"code": "print(1 + 1)"}'. Output is the job's execution history - stdout, stderr, timing, and artifacts - persisted in PostgreSQL and retrievable for replay or forking with the same code and inputs via the rerun/fork API.
Integrations
pip install "tako-vm[server]"
tako-vm setup                   # pull the executor Docker image
tako-vm server                  # start server (auto-starts PostgreSQL via Docker)
Requires Docker and Python 3.10+; the server auto-starts PostgreSQL via Docker. The CLI also covers tako-vm dev up (local PostgreSQL for development), tako-vm config, tako-vm validate, and tako-vm status. Apache License 2.0.
Who it's for
Teams deploying AI agents in production, including enterprise deployments, that need agents to execute code safely, with the surrounding job-queue, history, and replay infrastructure included rather than built from scratch.
Source README


A secure file system for your agents to execute code. Every job runs in its own isolated Docker container, with an ephemeral workspace, optional gVisor sandboxing, job queues, retries, and execution history included.
Where this is headed: durable, per-agent workspaces that persist and rehydrate across runs, a serverless filesystem for agents. Today each container is single-use; persistent workspaces are on the roadmap. gVisor remains the sole isolation boundary.
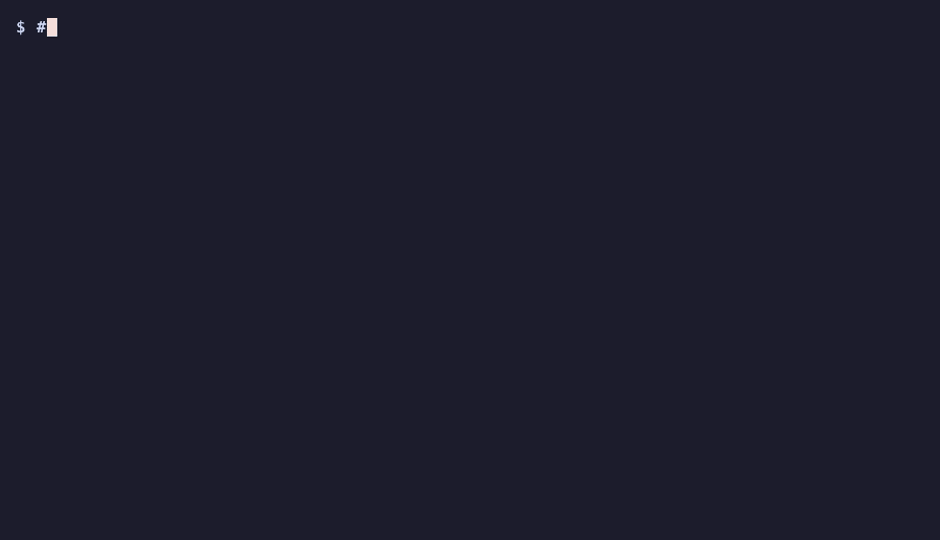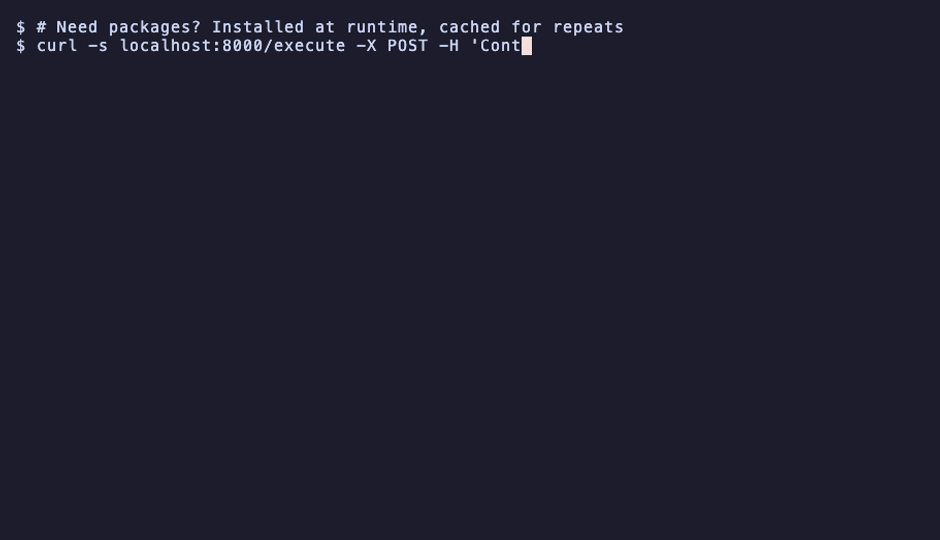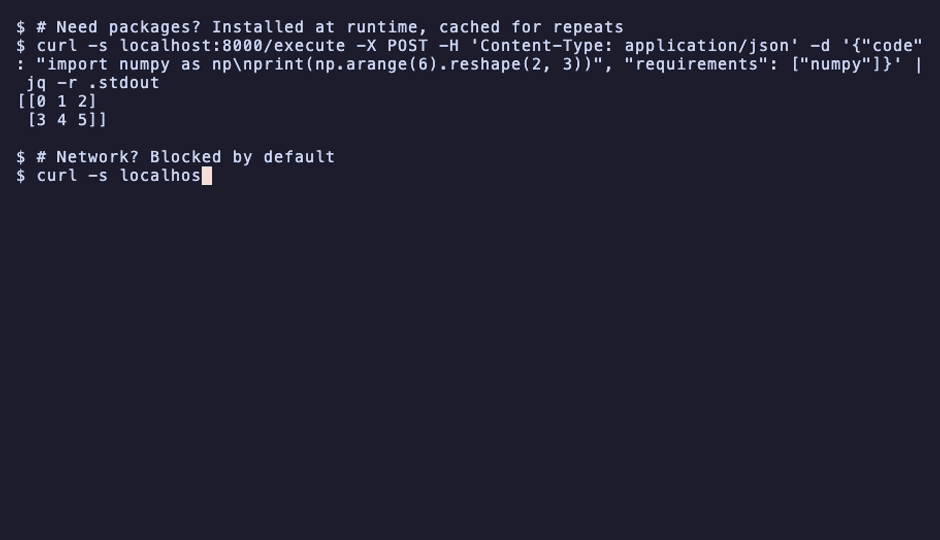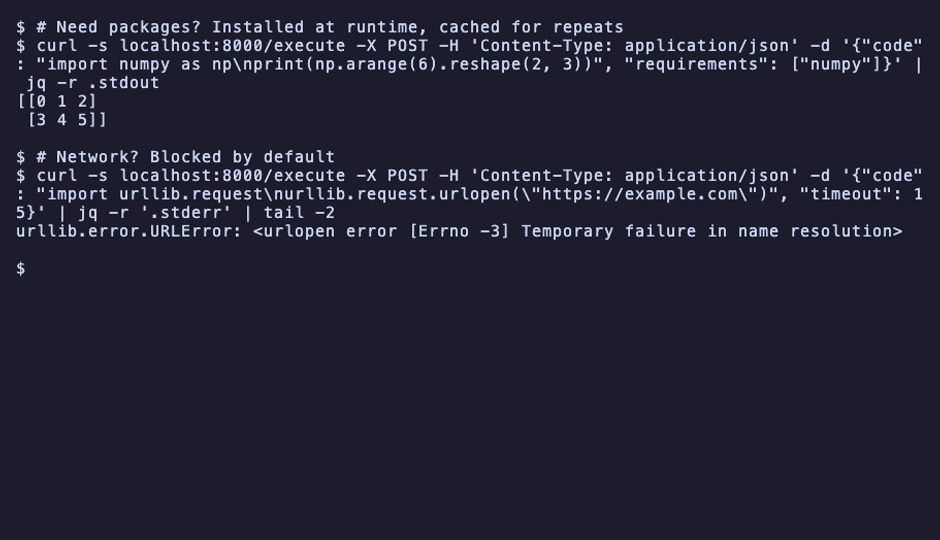
# Install (requires Docker + Python 3.10+)
pip install "tako-vm[server]"
tako-vm setup                   # pull the executor Docker image
tako-vm server                  # start server (auto-starts PostgreSQL via Docker)
# Execute code
curl -X POST http://localhost:8000/execute \
  -H "Content-Type: application/json" \
  -d '{"code": "print(1 + 1)"}'
Why Tako VM?
Sandbox solutions like e2b, daytona and microsandbox give you isolated code execution, but that's it. You still need to build:
| You build | With sandbox-only | With Tako VM |
|---|---|---|
| Job queue | Redis + Celery/Bull | Built-in |
| Execution history | Postgres + schema | PostgreSQL included |
| Retry logic | Custom code | Automatic |
| Idempotency | Deduplication logic | idempotency_key |
| Replay/debugging | Custom tooling | Rerun/fork API |
Tako VM is the complete package:
- Job queue + workers - Async execution with worker pool, no Redis/Celery setup
- Execution history - Every job persisted with stdout, stderr, timing, artifacts
- Replay to debug - Rerun past jobs with exact same code and inputs
- Docker isolation - Each job in its own container with seccomp filtering
- Network isolation - No network by default, optional allowlist per job type
- Self-hosted - Your machine, offline-capable, zero per-execution cost
CLI
tako-vm setup                     # Pull executor image and verify Docker
tako-vm server                    # Start the API server
tako-vm server --port 9000        # Custom port
tako-vm dev up                    # Start local PostgreSQL for development
tako-vm dev up --with-server      # Start PostgreSQL + API server
tako-vm dev status                # Check local PostgreSQL status
tako-vm dev down                  # Stop local PostgreSQL
tako-vm config                    # Show current configuration
tako-vm config --json             # Output as JSON
tako-vm validate                  # Validate current config
tako-vm validate my.yaml          # Validate specific file
tako-vm status                    # Check server health
tako-vm version                   # Show version
tako-vm --config my.yaml server   # Use specific config file
Documentation
| Topic | Link |
|---|---|
| Installation | docs/getting-started/installation.md |
| Quick Start | docs/getting-started/quickstart.md |
| Configuration | docs/getting-started/configuration.md |
| REST API | docs/api/rest.md |
| Python SDK | docs/api/sdk.md |
| Job Types & Environments | docs/guide/environments.md |
| Filesystem, Caches & ML Models | docs/guide/filesystem-and-caches.md |
| Security | docs/deployment/security.md |
| Deployment | docs/deployment/how-to-deploy.md |
| Config Reference | tako_vm.yaml.example |
Security
Tako VM runs untrusted, often AI-generated, code, so isolation is the core of the project. It uses layered defenses: gVisor (userspace kernel), per-job ephemeral Docker containers, a default-deny seccomp profile, network isolation (--network=none by default), capability dropping, non-root execution, and enforced resource and input limits.
security_mode: strict with container_runtime: runsc is the default: Tako VM refuses to start a job rather than run it without the gVisor userspace-kernel boundary. Set security_mode: permissive to allow a fallback to standard Docker (runc) on hosts without gVisor, e.g. local development or CI; that fallback removes the userspace-kernel boundary, so do not use it for untrusted code.
See SECURITY.md for the threat model and hardening guidance, and docs/deployment/security.md for full details.
Found a vulnerability? Report it privately via the Security tab → Report a vulnerability. Please do not open public issues for security findings.
FAQ
Common questions
Discussion
Questions & comments · 0
Sign In Sign in to leave a comment.