
Share temporary files securely between AI agents and humans
aispace is a scriptable CLI for secure, expiring file handoffs between AI agents and humans, with predictable JSON and local encryption.
0.4.1Add to Favorites
Why it matters
Enable AI agents and automation scripts to hand off generated files-reports, archives, images, structured data-to humans or other systems through expiring links with optional encryption, without cluttering chat interfaces or permanent storage.
Outcomes
What it gets done
Upload files from CLI or stdin with predictable JSON output for agent parsing
Generate expiring public share links with download caps and revocation controls
Encrypt files locally with age X25519 before upload, keeping decryption keys private
Manage file lifecycle with authenticated access, account sharing, and automatic expiration
Source
Get it from source
Spark does not host a copy of it.
Open sourceReports
Agent outcome reports
No reports yet
Overview
aispace is a scriptable CLI for secure, temporary file sharing between AI agents and humans, with expiring links, predictable JSON output, and optional local age encryption. It also exposes ten typed MCP tools over local stdio for direct agent integration. Reach for it when an AI agent needs to hand off a generated file too large for chat, with an expiring, revocable link and machine-parseable JSON.
What it does
aispace is a secure temporary file-sharing CLI built for AI agents and humans, for outputs too large, structured, or temporary for chat. It ships as one binary with stable exit codes, streaming uploads, and share URLs printed on a predictable final line, so a script or agent can capture the result without parsing free text. Every supported command can return stable JSON (--json), with structured errors on stderr and explicit noninteractive flags for automation; secret-bearing handoff commands stay interactive by design. Files and links are short-lived by design - separate file expiration, separately expiring public links, revocation, and optional per-link download caps - and sealed asynchronous transfers encrypt filenames, metadata, and content locally, with the master key never reaching aispace's servers; an age X25519 flow remains available for recipient-key workflows. Sealed transfers, agent identities, device pairing, and adaptive durable-first intent are marked experimental; ordinary uploads and durable R2 storage are stable. The repository is the open-source client, an agent skill, and integration examples - the hosted service, billing, and deployment configuration are operated separately.
When to use - and when NOT to
Use it when an AI agent (or a human) needs to hand off a generated artifact - a report, archive, image, or other output - that is too large or structured for chat, and you want expiring, revocable links with predictable JSON output an agent can parse. Sealed multi-file transfers, agent-to-agent recipient pinning, and device-pairing handoffs cover cases where you need authenticated delivery without exposing a bearer decryption link.
Public links require a Pro account and max out at 30 days; files themselves default to 7-day expiration (max 7 days on Free, 30 on Pro). Sealed transfers, agent identities, device pairing, and adaptive durable-first intent are explicitly experimental surfaces, so treat them as less stable than ordinary uploads. AISPACE_AGE_IDENTITY and transfer secrets are deliberately not accepted as command-line argument values, to avoid leaking them on shared systems through process listings.
Inputs and outputs
Input is a file path or stdin (aispace upload - --name note.txt); output is a JSON object on --json ({"file": File, "link": ShareLink}, with an "encryption" object added for encrypted uploads) or a plain share URL printed last on its own line. Errors are written to stderr, either as error: <message> (<code>) or, with --json, as {"error":{"code","message","status","details","exit_code"}}. Exit codes are stable: 0 success, 1 generic error, 2 usage error, 3 authentication, 4 quota/size, 5 rate limited (idempotent GETs sleep Retry-After, max 30s, and retry once).
Integrations
curl -fsSL https://aispace.sh/install.sh | sh
Also installable via npm install -g @aispace-sh/cli, brew install aispace-sh/tap/aispace, or go install github.com/aispace-sh/aispace-client@latest; release binaries cover macOS, Linux, and Windows on amd64 and arm64. The native CLI exposes ten typed MCP tools over local stdio (aispace mcp serve), configurable in Codex with per-tool approval modes for aispace_create_link, aispace_revoke_link, and aispace_delete_file; the ChatGPT desktop app, Codex CLI, and Codex IDE extension on the same host share that configuration, and Claude Code examples are documented separately. A reusable Codex-compatible skill ships in the repo (symlink skills/aispace into ~/.codex/skills), and docs/LLM_USAGE.md provides a system-prompt snippet, OpenAI/Anthropic-compatible tool schemas, and a reference Python handler for custom agent runtimes. Written in Go (1.26+), MIT licensed.
Who it's for
Developers building AI agents that need to hand off files, reports, or other generated artifacts to a human or another agent - with expiring links, predictable JSON, and optional local encryption - rather than pasting large outputs into chat.
Source README
aispace


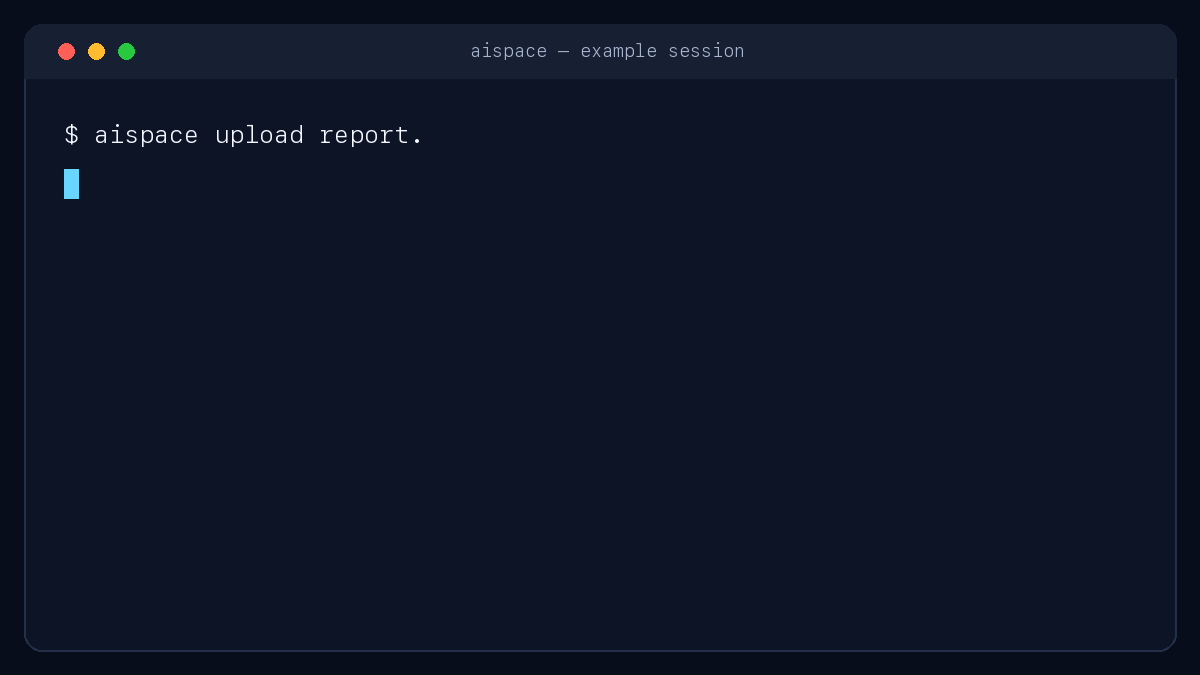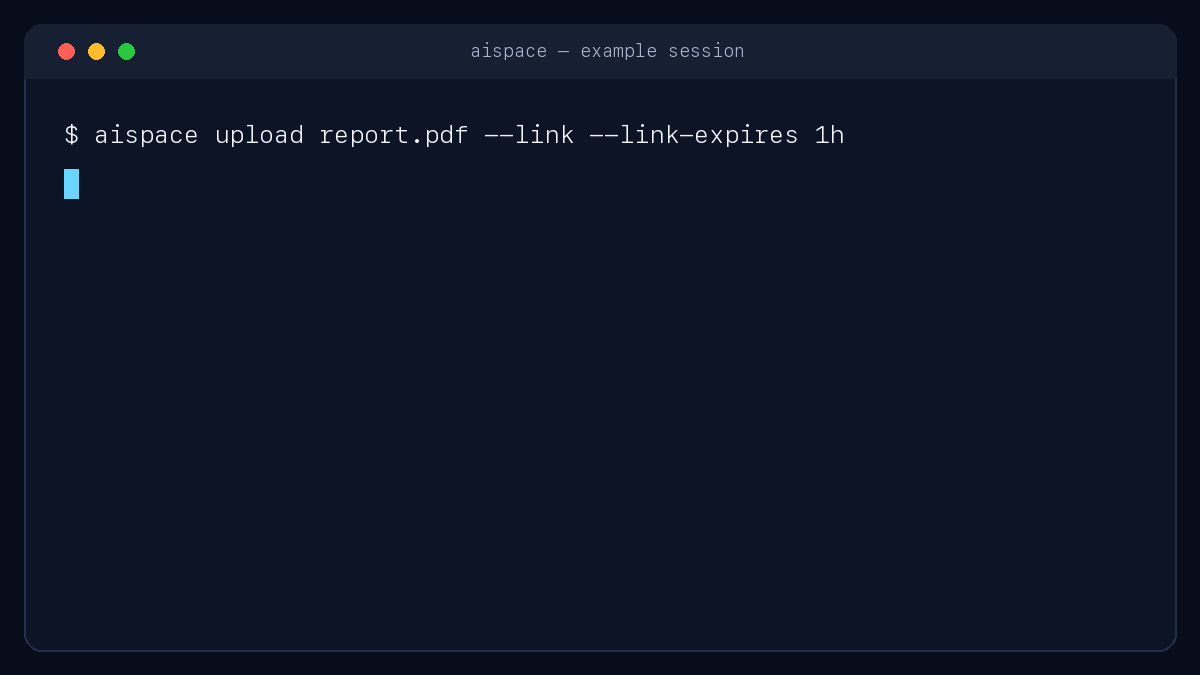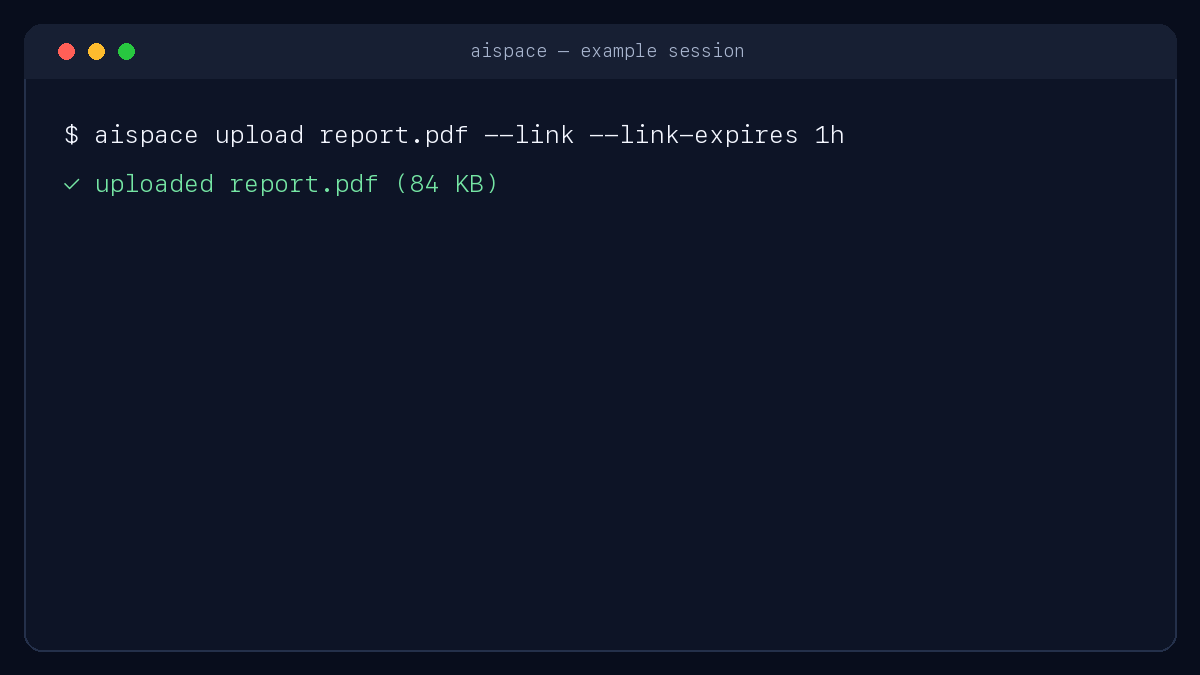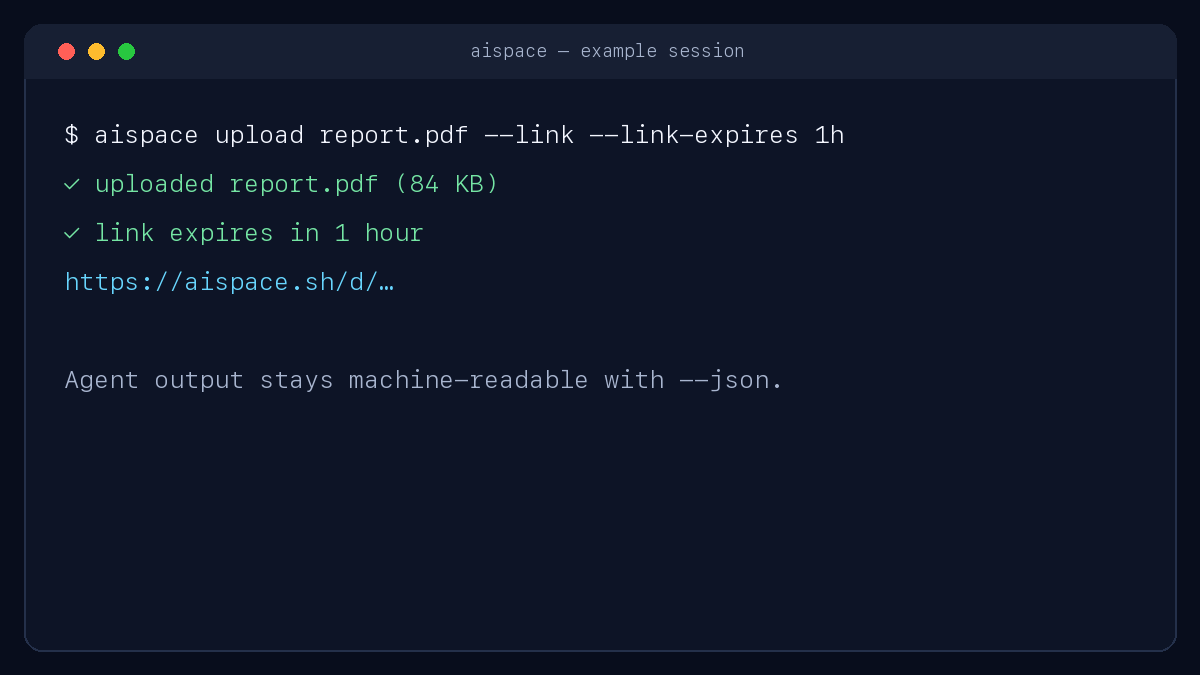
aispace.sh is a bot-friendly file drop for outputs that are too large, structured, or temporary for chat. The open-source client is deliberately easy to automate: one binary, stable exit codes, streaming uploads, and share URLs printed on a predictable final line.
- Built for agents: stable JSON on supported commands, documented errors, stdin support, and explicit noninteractive flags for automation. Secret-bearing handoff commands remain interactive.
- Short-lived by design: file expiration, separately expiring links, revocation, and optional per-link download caps.
- Private when needed: sealed asynchronous transfers encrypt filenames, file metadata, and content locally; their master key never reaches aispace. The existing age X25519 flow remains available for recipient-key workflows.
Sealed transfers, agent identities, device pairing, and adaptive durable-first intent are experimental surfaces. Ordinary uploads and durable R2 storage continue to work alongside them.
The hosted service is operated separately. This repository contains the client, agent skill, and integration examples-not the server, billing system, deployment configuration, or customer data.
Try it in 60 seconds
Install the latest release:
curl -fsSL https://aispace.sh/install.sh | sh
Authenticate with a key created in the aispace dashboard, then store a file:
aispace login --key ask_...
aispace upload report.pdf --json
On a Pro account, add a separately expiring public handoff:
aispace upload report.pdf --link --link-expires 1h --max-downloads 1
The URL is printed last on its own line, making it easy for an agent or shell script to capture.
Add --json for a stable machine-readable response. An abridged response looks like:
{"file":{"id":"...","name":"report.pdf"},"link":{"url":"https://aispace.sh/d/...","expires_at":1757003600}}
Other installation channels:
npm install -g @aispace-sh/cli
brew install aispace-sh/tap/aispace
go install github.com/aispace-sh/aispace-client@latest
Pin the shell installer with AISPACE_VERSION=v1.2.3. Release binaries support macOS, Linux, and
Windows on amd64 and arm64. The shell installer supports macOS and Linux; use npm on Windows.
Using Grok Bot?
Give aispace to an agent
The repository includes a reusable Codex-compatible skill. Clone the repository and link the skill into your personal Codex skills directory:
git clone https://github.com/aispace-sh/aispace-client.git
mkdir -p ~/.codex/skills
ln -s "$PWD/aispace-client/skills/aispace" ~/.codex/skills/aispace
Restart Codex, then ask it to use aispace when it needs to hand you a report, archive, image, or
other generated artifact. The skill defaults to account-private storage unless you request a public
link, prefers short expirations, and treats encryption identities as credentials.
Model Context Protocol (MCP)
The native CLI also exposes ten typed MCP tools over local stdio. Create a separately scoped bot key in the dashboard, export it in the environment that launches Codex, and add:
[mcp_servers.aispace]
command = "aispace"
args = ["mcp", "serve"]
env_vars = ["AISPACE_KEY", "AISPACE_URL", "AISPACE_ALLOWED_ROOTS"]
startup_timeout_sec = 10
tool_timeout_sec = 120
default_tools_approval_mode = "writes"

[mcp_servers.aispace.tools.aispace_create_link]
approval_mode = "prompt"

[mcp_servers.aispace.tools.aispace_revoke_link]
approval_mode = "prompt"

[mcp_servers.aispace.tools.aispace_delete_file]
approval_mode = "prompt"
Run codex mcp list to verify the connection. The ChatGPT desktop app, Codex CLI, and Codex IDE
extension on the same host share this configuration. Keep the key in a secret store or injected
environment; never put its expanded value in a committed project file or command argument. See
docs/CLI.md for Claude Code and generic-host examples.
For custom agent runtimes, docs/LLM_USAGE.md includes a system-prompt snippet,
OpenAI/Anthropic-compatible tool schemas, and a reference Python handler. See examples
for runnable shell, CI, and encrypted-handoff recipes.
Common workflows
# Upload text from stdin and return an expiring public link (Pro).
echo "hello" | aispace upload - --name note.txt --link --link-expires 1h

# Keep a file available only to this key.
aispace upload secret.txt --private

# Share ciphertext; keep the generated age identity locally.
aispace upload secret.pdf --encrypt --identity-out secret.agekey --link

# Authenticated handoff to another key on the same account—no public URL.
aispace upload notes.md --shared --json

# Sealed multi-file handoff. The URL fragment holds the local decryption secret.
aispace transfer create report.pdf charts.png --sealed --link --expires 1d --max-downloads 1

# Move that sealed transfer to a nearby browser/device with an expiring code.
aispace handoff offer "$TRANSFER_ID"
# On the receiving CLI: aispace handoff receive J7KM-PQRT

# Pin an agent and deliver without exposing a bearer decryption link.
aispace recipient add "$RECIPIENT_INVITATION"
aispace recipient verify research-agent --fingerprint "$RECIPIENT_FINGERPRINT"
aispace transfer create report.pdf --sealed --to research-agent --from my-agent --expires 7d
aispace inbox receive "$DELIVERY_ID" --yes

# Paste the link interactively, inspect its private manifest, then decrypt and verify.
aispace transfer receive

# Receive, manage, and revoke.
aispace ls --json
aispace download <file_id> --output ./file
aispace download <file_id> --output ./file --verify   # check the recorded SHA-256
aispace link <file_id> --expires 30m --max-downloads 1
aispace revoke <link_id>
aispace rm <file_id>
Follow docs/SECURE_HANDOFFS.md for sealed bundles, trusted agent
inboxes, device pairing, adaptive R2 fallback, and recovery. The complete command reference is in
docs/CLI.md; the HTTP contract is in docs/API.md.
upload accepts --name, --expires, --content-type, --sha256, --link, --link-expires,
--max-downloads, --private, --shared, --encrypt, --recipient, and --identity-out.
Uploads stream from disk. Encrypted uploads use age X25519 locally and store ciphertext as
<name>.age; the secret identity is never sent to the API.
transfer create uses aispace-sealed-v1: AES-256-GCM authenticated chunks and an encrypted
manifest support multiple files, ranged retry, and a verified receipt. transfer receive accepts
the secret from its prompt, --token-file, or AISPACE_TRANSFER_TOKEN; avoid putting a full
fragment link or token in a process argument on shared systems.
transfer create --json omits bearer links and tokens unless --include-secret is explicit, and
secret-inclusive JSON must be redirected rather than written to a terminal. handoff encode
likewise accepts the protected prompt, --token-file, or AISPACE_TRANSFER_TOKEN.
With --json, errors also remain structured and are written to stderr. upload --link --json
returns {"file": File, "link": ShareLink}; encrypted uploads add an "encryption" object.
Configuration
Precedence: flag > environment > config file > default.
| Setting | Flag | Env | File key | Default |
|---|---|---|---|---|
| API key | --key |
AISPACE_KEY |
key |
- |
| Server | --url |
AISPACE_URL |
url |
https://aispace.sh |
AISPACE_AGE_IDENTITY supplies a decryption identity when decrypt --identity-file is omitted.
It is deliberately not accepted as a command-line value.
Config file: $XDG_CONFIG_HOME/aispace/config.json (default ~/.config/aispace/config.json), written with
mode 0600. A warning is printed if the file is readable by others. AISPACE_CONFIG overrides the path.
Durations (--expires, --link-expires) accept Go syntax plus a d suffix: 30m, 24h, 7d, 1d12h,
or a bare number of seconds. Omitting them uses the server defaults (7 days for files, 1 hour for
Pro public links).
File permissions and links
File visibility controls authenticated key access. A public link is a separate capability: creating one requires a Pro account and makes that one file available to anyone holding the URL.
| File mode | Who can access it? | File lifetime | Public-link lifetime | Download cap | Exposure if access leaks |
|---|---|---|---|---|---|
private |
Uploading key only | 7 days by default; maximum 7 days on Free or 30 days on Pro | None | Account monthly limit | Private files belonging to that key, until deletion or expiry |
account |
Every active key on the account | 7 days by default; maximum 7 days on Free or 30 days on Pro | None | Account monthly limit | Account-shared files, until deletion or expiry |
private + public link |
Uploading key and anyone with the URL | Maximum 30 days because links require Pro | 1 hour by default; maximum 30 days and never beyond file expiry | Optional per-link cap | Only the linked file, until link expiry, revocation, exhaustion, file deletion, or file expiry |
account + public link |
Account keys and anyone with the URL | Maximum 30 days because links require Pro | 1 hour by default; maximum 30 days and never beyond file expiry | Optional per-link cap | URL access ends with the link; account keys retain access until file deletion or expiry |
| Client-encrypted file | Visibility controls ciphertext access; only age identity holders can decrypt it | Same limits as the selected file mode | Same Pro-only limits when a link is created | Optional per-link cap | Plaintext exposure requires both the ciphertext and the age identity |
Available duration syntax includes 30s, 15m, 1h, 36h, and 7d.
A file becomes unavailable when its file lifetime ends. A link can end sooner because it expired, was revoked, or reached its download cap. Deleting the file immediately ends authenticated key access and every associated public link.
Exit codes
| Code | Meaning |
|---|---|
| 0 | success |
| 1 | generic error (network, 4xx/5xx not listed below) |
| 2 | usage error |
| 3 | authentication (401, or no key configured) |
| 4 | quota / size (402, 413) |
| 5 | rate limited (429) - idempotent GETs sleep Retry-After (max 30s) and retry once |
Errors go to stderr as error: <message> (<code>); with --json they are a JSON object
{"error":{"code","message","status","details","exit_code"}} on stderr instead.
Development
go test -race ./... && go vet ./... && test -z "$(gofmt -l .)"
go build -ldflags "-X main.version=0.0.0-dev" -o aispace .
(cd npm && npm test && npm pack --dry-run)
The test suite uses local HTTP fixtures and does not require an aispace key. Contributions are
welcome-start with CONTRIBUTING.md, check the ROADMAP.md, and
review the CHANGELOG.md. Focused bug reports and feature proposals can use the
repository's structured issue forms.
Releases are cut through the manual GitHub Actions workflow. GoReleaser builds checksummed macOS,
Linux, and Windows binaries, updates the Homebrew tap, publishes @aispace-sh/cli to npm, verifies
the installed MCP server on all three platforms, and finally publishes sh.aispace/mcp to the
official Registry. See RELEASE.md for publisher configuration, resumable MCP-only
publication, and the release checklist.
Security
Please report vulnerabilities privately through GitHub Security Advisories. Do not open a public
issue containing a credential, private link, or customer data. See docs/SECURITY.md.
FAQ
Common questions
Discussion
Questions & comments · 0
Sign In Sign in to leave a comment.